By Brian Mahon
Let’s be honest. Most business owners would rather talk about almost anything other than cyber insurance.
Cybersecurity feels technical, confusing, and frankly, a little overwhelming. The good news is that cyber insurance isn’t really about technology. It’s about protecting your business financially when something goes wrong.
The easiest way I explain cyber insurance is this: remember those old Staples commercials with the big red “Easy Button”?
Cyber insurance is the closest thing businesses have to an easy button when a cyberattack happens.
When you buy a cyber insurance policy, you’re not just buying a check. You’re buying access to an entire team of experts that springs into action the moment something goes wrong. Most policies include a 24/7 incident response hotline staffed by breach coaches, who are typically specialized privacy attorneys. Think of them as the quarterback of your cyber response team.
The first question they’re trying to answer is simple: What happened?
Was it ransomware? Did someone steal data? Did an employee click a phishing email? Did money leave the company through a fraudulent wire transfer? Did customer information get exposed?
From there, the breach coach starts calling the plays.
They may bring in a forensic IT firm to determine how the attackers got in, what they accessed, and whether sensitive information was compromised. If customer information was exposed, they may coordinate credit monitoring services, call centers, legal guidance, notification requirements, and public relations support.
If ransomware is involved, they may engage negotiators. If regulators get involved, they help coordinate legal defense. If your business is shut down for several days, business interruption coverage may help replace lost income and keep the lights on while you recover.
In short, cyber insurance helps your business get back on its feet while experienced professionals handle the chaos.
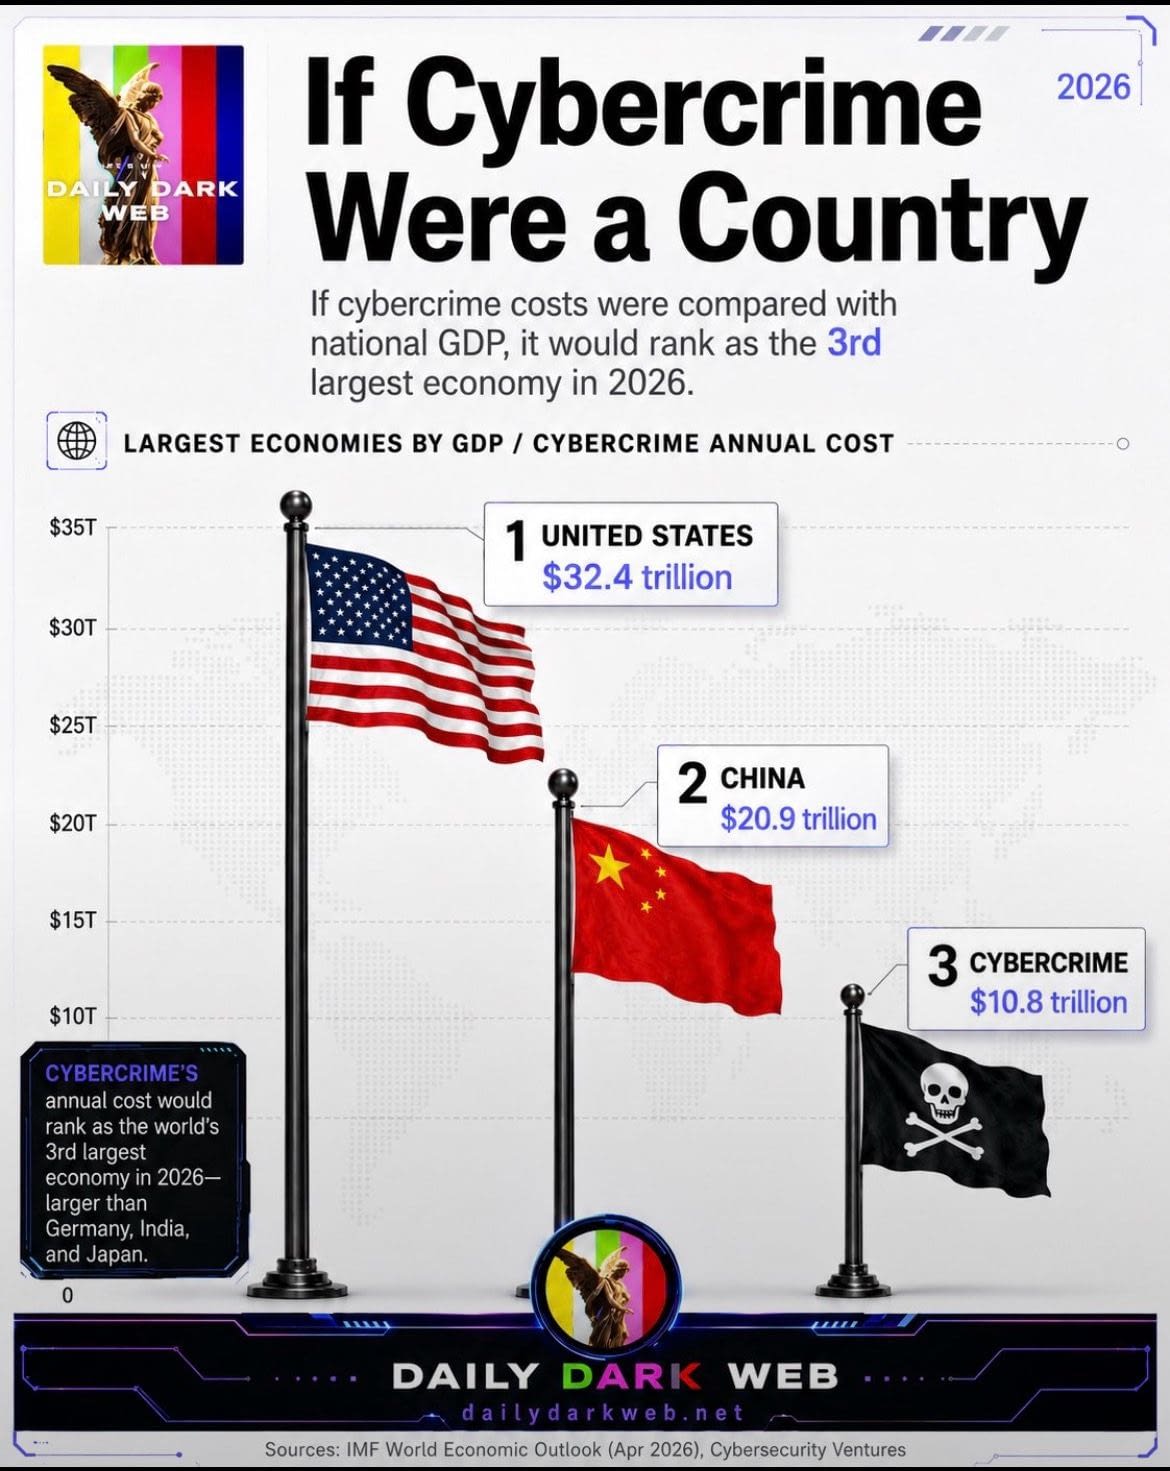
The Problem Is Bigger Than Most Business Owners Realize
A lot of business owners still picture cybercriminals as hackers sitting in dark basements targeting Fortune 500 companies.
That’s not how it works anymore.
Most cyberattacks today are automated. Criminals send millions of phishing emails, scan the internet for vulnerabilities, buy stolen passwords, and use ransomware kits that can be deployed with very little technical expertise.
Think of it like a thief walking through a neighborhood checking for unlocked doors.
They’re not targeting a specific house.
They’re looking for the easiest house.
Unfortunately, many small businesses fit that description.
Six Cyber Insurance Myths I Hear Every Week
Myth #1: “I Can’t Afford Cyber Insurance”
This is probably the biggest misconception I encounter.
Cyber insurance is often far less expensive than business owners expect.
Many solo entrepreneurs can purchase $1 million in cyber coverage for under $1,000 per year. Even manufacturers, contractors, distributors, and other larger companies are often surprised by how affordable coverage can be relative to the risk.
When you compare that to the cost of a ransomware attack, legal fees, forensic investigations, customer notifications, and lost revenue, the math becomes pretty straightforward.
Myth #2: “I Don’t Know What My Cyber Risk Is”
The reality is that you don’t need to hire a six-figure consulting firm to get a basic understanding of your cyber exposure.
There are plenty of free resources available from organizations such as BitSight, SecurityScorecard, NetDiligence, IBM, and the Ponemon Institute.
One of my personal favorites is Chubb’s Cyber Risk Index because it helps business owners start thinking about cyber risk in practical business terms rather than technical jargon.
You don’t have to become a cybersecurity expert overnight. You just need to understand where your biggest vulnerabilities may exist.
Myth #3: “We’re Too Small to Be Targeted”
Cybercriminals love this myth.
The truth is many attackers actually prefer smaller businesses because they often have fewer cybersecurity controls and less monitoring.
More importantly, small businesses are frequently connected to larger organizations.
Think about all the local companies supporting Pennsylvania state agencies, healthcare organizations, banks, manufacturers, school districts, and other critical institutions. Criminals often view smaller vendors as a pathway into larger networks.
You may think you’re too small to matter.
The attacker may see you as the weakest link in a much bigger chain.
Myth #4: “Our Security Is Strong Enough, So We Don’t Need Insurance”
Good cybersecurity is incredibly important.
But even the best defenses can’t eliminate risk entirely.
People still click links.
Employees still make mistakes.
Software still contains vulnerabilities.
New attack methods emerge every day.
Cyber insurance isn’t a replacement for cybersecurity. It’s the financial backup plan when cybersecurity fails.
In fact, most cyber insurance carriers require strong security controls like multi-factor authentication, endpoint protection, employee training, and backups before they will even offer coverage.
The best cybersecurity strategy is a combination of prevention and preparation.
Myth #5: “My General Liability Policy Already Covers This”
In most cases, it doesn’t.
This is one of the most dangerous misunderstandings in commercial insurance today.
Traditional general liability and business owner’s policies were designed to cover things like slip-and-fall injuries, property damage, and other traditional business risks.
They were not built to handle ransomware attacks, fraudulent wire transfers, business email compromise, or modern cybercrime.
Some policies have cyber endorsements, but many offer very limited protection and often miss the types of losses we see most frequently.
If you’re relying on your general liability policy to handle a major cyber event, you should verify exactly what is and is not covered before an incident occurs.
Myth #6: “Our Data Is in the Cloud, So It’s Not Our Problem”
I hear this one all the time.
Many business owners assume that because their data is stored in Microsoft Azure, Amazon Web Services, Google Cloud, or another cloud platform, the provider is responsible for everything.
That’s not how cloud security works.
The cloud provider is typically responsible for securing its infrastructure. You are still responsible for securing your users, passwords, permissions, data, and configurations.
Don’t believe me? Open your cloud provider’s terms of service.
You’ll find language that essentially says: you are responsible for protecting and backing up your data.
If customer information is exposed, regulators and affected customers aren’t going to care whose server the data was sitting on. They’re going to look to the business that collected the information.
Cyber Risk Is a Business Risk
Cybersecurity is no longer just an IT issue.
It’s a business issue.
The financial impact of a cyber incident can be devastating, particularly for small and midsize businesses. Strong cybersecurity controls are critical, but they’re only part of the solution.
Cyber insurance provides something every business owner hopes they’ll never need: a team of experts and financial resources ready to respond when a bad day becomes a really bad day.
And if that day ever comes, having an “easy button” can make all the difference.
About the Author
Brian Mahon, CIC, CRM, CCIC, is the founder of Igloo Insurance and specializes in cyber insurance, cyber liability, and technology-related risk management for businesses throughout Pennsylvania.
Mahon has spent more than a decade working in both the cybersecurity and property & casualty insurance industries. He holds the Certified Insurance Counselor (CIC), Certified Risk Manager (CRM), and Cyber COPE Insurance Certification (CCIC) designations through Chubb and Carnegie Mellon University’s Heinz College of Information Systems.
A resident of Lititz and father of two, he operates Igloo Insurance in Central Pennsylvania and is currently completing his MBA at Penn State Harrisburg.